Best SIEM Tools and How They Improve Threat Detection & Response
By: Ganesan D
15 Nov 2025
Category: Security Operation
15 Nov 2025
Category: Security Operation
Introduction
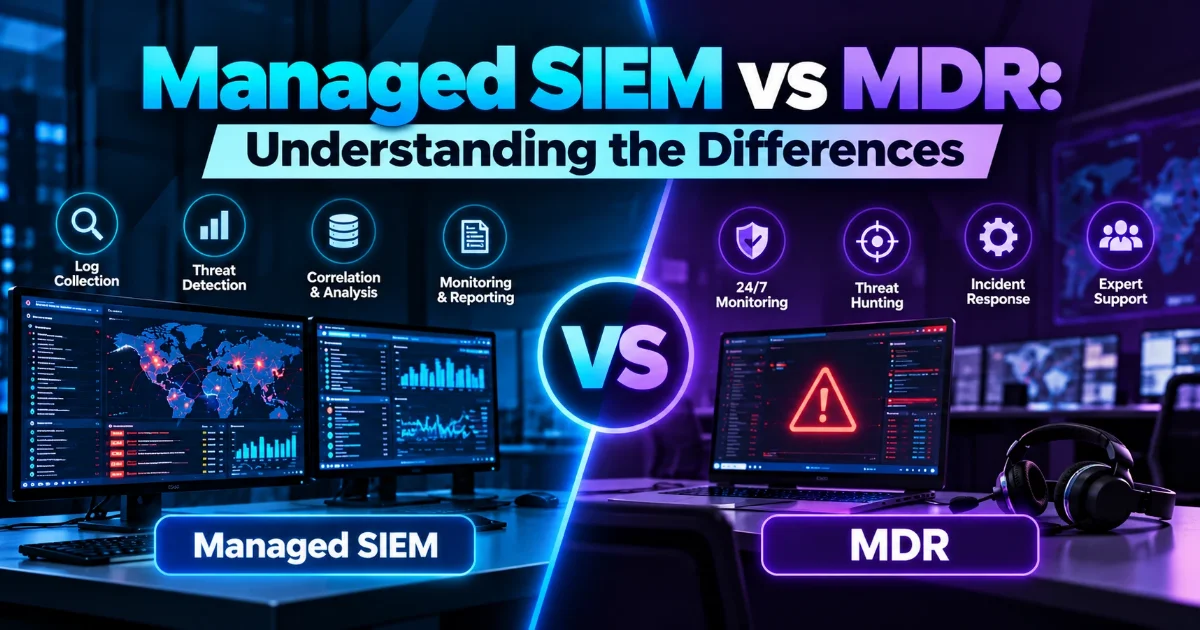
In today’s world of constant cyber threats, organisations cannot rely on manual monitoring or basic firewalls. SIEM (Security Information and Event Management) tools provide a complete, real-time view of activity across endpoints, networks, cloud apps, and servers — helping security teams detect, analyse, and respond to threats quickly and accurately.
Below are some of the top SIEM tools and how they improve security operations.
1. Splunk Enterprise Security
How it helps: Splunk uses AI and advanced analytics to analyse massive amounts of log data instantly and identify unusual patterns.
- Detects anomalies using machine learning
- Provides visual dashboards for faster investigation
- Supports automated playbooks for instant response
Example: Multiple failed logins followed by sensitive file access triggers Splunk to disable the account automatically.
2. IBM QRadar
How it helps: QRadar correlates logs from different systems to detect complex, multi-stage attacks.
- Detects advanced threats across multiple systems
- Automatically prioritises incidents by severity
- Integrates with IBM SOAR for automated response
Example: QRadar links unusual database queries with USB activity to flag an insider threat.
3. Microsoft Sentinel
How it helps: A cloud-native SIEM integrated with Azure and Microsoft 365 for AI-powered threat analytics.
- Built-in threat intelligence for detecting malicious IPs
- Automated investigation workflows
- Correlates on-prem and cloud data seamlessly
Example: Detects ransomware patterns and isolates the device automatically.
4. LogRhythm NextGen SIEM
How it helps: Combines SIEM, UEBA, and SOAR for advanced behavioural detection and automation.
- Detects insider threats using behaviour analytics
- One-click automated response workflows
- Fast forensic search for root-cause analysis
Example: Flags suspicious large data downloads and begins an automated investigation.
5. AlienVault (AT&T Cybersecurity)
How it helps: Combines SIEM with vulnerability assessment and threat intelligence.
- Detects threats using global threat feeds
- Correlates known attack patterns
- Provides guided response actions
Example: Blocks communication with known malicious IPs automatically.
6. ArcSight (Micro Focus)
How it helps: Known for scalability and real-time correlation ideal for large enterprises.
- Processes millions of logs per second
- Identifies hidden multi-stage attacks
- Integrates with external response tools
Example: Detects phishing → malware → privilege escalation attack chains in real time.
How These Tools Improve Threat Management
| Key Function |
How It Helps |
| Real-Time Monitoring | Tracks all activity continuously |
| Threat Correlation | Combines small alerts into real threats |
| Automation & SOAR | Instant response to contain attacks |
| Behavior Analytics (UEBA) | Detects unusual user behaviour |
| Incident Prioritisation | Focus on high-risk threats first |
| Threat Intelligence | Blocks global malicious IPs/domains |
Example Scenario
A hacker tries to access your HR portal using stolen credentials:
- Splunk detects repeated failed logins
- QRadar connects it with a suspicious VPN login
- Sentinel disables the user account automatically
- LogRhythm runs an automated investigation
Result: Attack contained within minutes — before any data breach.
Final Thoughts
SIEM tools are the backbone of modern cyber defence. Whether you choose Splunk, QRadar, Sentinel, or LogRhythm — the right SIEM transforms raw data into actionable intelligence, helping your organisation detect threats faster and respond more effectively.