Manual vs Automated Web Application Penetration Testing
By:
Ganesan D
28 Sep 2026
Category:
Penetration Testing
Introduction
Organizations use Web App Pentesting to identify and validate these security weaknesses. Two common approaches are manual testing and automated testing. While automated tools can quickly identify many common vulnerabilities, manual testing can uncover complex weaknesses that require human analysis and understanding of application behavior.
Understanding the differences between manual and Automated Web Application Penetration Testing can help security teams develop a more effective application security testing strategy.
What is Manual Web Application Penetration Testing?
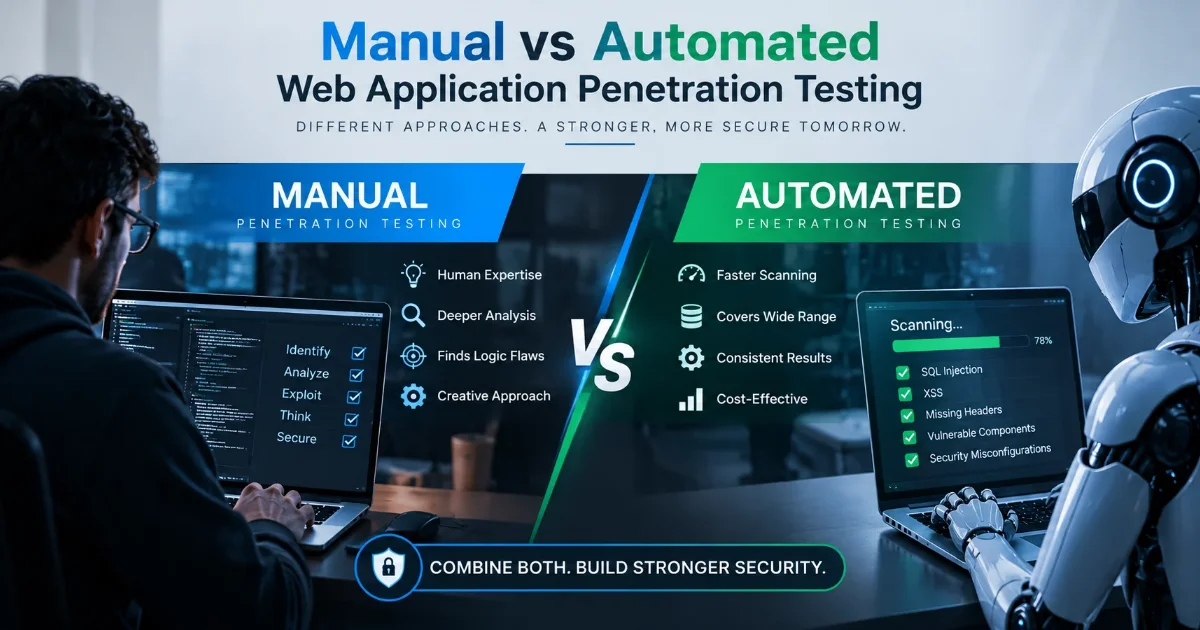
Manual penetration testing involves security professionals examining and testing an application using their knowledge, experience, and specialized testing techniques.
Manual testing can be particularly useful for identifying:
- Business logic vulnerabilities
- Complex access control issues
- Authentication and authorization weaknesses
- Session management problems
- API security issues
- Multi-step attack scenarios
- Application-specific security flaws
Because manual testing involves human analysis, testers can adapt their approach based on how the application responds during the assessment.
What is Automated Web Application Penetration Testing?
Automated Web Application Penetration Testing uses specialized software and Web Application Penetration Testing Tools to scan applications for known vulnerabilities, security weaknesses, and configuration issues.
Common automated testing capabilities include:
- Vulnerability scanning
- Security misconfiguration detection
- Identification of outdated components
- Detection of common injection vulnerabilities
- Discovery of exposed endpoints
- Automated crawling of application functionality
- Repeated security checks
Automation can help security teams perform testing more frequently and efficiently, particularly across large application environments.
Key Differences
Neither approach completely replaces the other. They address different aspects of Application Pentesting.
| Factor |
Manual Testing |
Automated Testing |
| Approach |
Human-led analysis |
Tool-driven analysis |
| Speed |
Generally slower |
Generally faster |
| Coverage |
Deep analysis of selected areas |
Broad coverage of many components |
| Business Logic |
Strong capability |
Limited in many cases |
| Scalability |
More resource-intensive |
Highly scalable |
| False Positives |
Can be reduced through human validation |
May require manual verification |
| Complex Attack Chains |
Better suited |
Limited depending on the tool |
| Repeatability |
Requires tester involvement |
Highly repeatable |
| Human Expertise |
Essential |
Less dependent for initial scanning |
Advantages and Limitations
Manual Testing Advantages
Manual testing provides flexibility and contextual analysis. Experienced testers can understand how application functionality works and develop testing scenarios based on observed behavior.
It is particularly valuable when testing complex workflows, authorization controls, APIs, and business logic.
Limitations
Manual testing can require more time, skilled security professionals, and resources. It may also be difficult to perform at the same scale as automated scanning across very large applications.
Automated Testing Advantages
Automation provides speed, scalability, and repeatability. A security team can use Web Application Penetration Testing Tools to scan large application environments and perform recurring checks.
Automated testing can also be useful during development and continuous security monitoring processes.
Limitations
Automated tools may not understand an application's unique business rules or complex workflows. They can also generate false positives or miss vulnerabilities that require contextual analysis and creative testing.
When Should You Use Each Approach?
Use Automated Testing When:
- You need to scan large application environments
- You want frequent security checks
- You need to identify common vulnerabilities quickly
- You want repeatable testing during development
- You need an initial overview of the application's security posture
Use Manual Testing When:
- The application contains complex business logic
- You need deeper authorization testing
- The application handles sensitive information
- You need to test complex workflows or attack chains
- Automated results require deeper validation
For high-risk applications, relying exclusively on either approach can leave important testing gaps.
Why Combine Both Approaches?
Combining manual and automated testing can improve overall Web App Pentesting coverage.
A combined approach can provide:
- Broader vulnerability coverage
- Faster identification of common weaknesses
- Deeper analysis of complex vulnerabilities
- Better validation of automated findings
- More effective testing of business logic
- Improved confidence in security assessment results
For example, an automated scanner may identify a potentially vulnerable endpoint, while a security professional can manually investigate how that endpoint interacts with authentication, authorization, and business workflows.
Conclusion
Manual vs Automated Web Application Penetration Testing is not necessarily an either-or decision. A well-designed Application Pentesting strategy can combine both approaches to improve coverage and identify a wider range of security weaknesses.
Organizations should consider the application's risk, complexity, technology, development lifecycle, and security requirements when determining the appropriate testing approach. Combining Web Application Penetration Testing Tools with experienced manual testing can provide a more comprehensive assessment of an application's security.