How to Prepare Your Organization for a Red Team Assessment
By: Ganesan D
17 Sep 2026
Category:
Penetration Testing
Introduction
Organizations invest heavily in firewalls, endpoint security, identity controls, monitoring platforms, and other cybersecurity technologies. However, having security controls in place does not necessarily mean they will perform effectively during a real cyberattack.
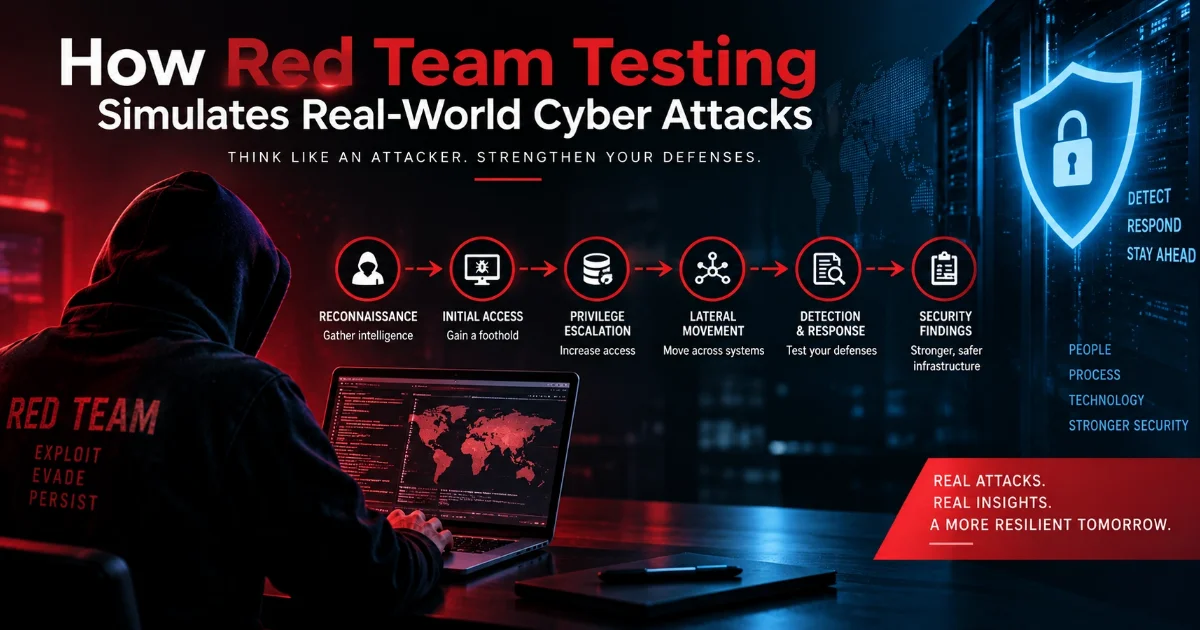
A Red Team Assessment provides an opportunity to evaluate an organization's defensive capabilities through a controlled simulation of realistic attack scenarios. It can help security teams understand how an attacker might attempt to gain access, move through the environment, reach critical assets, and avoid detection.
Define Objectives
The first step in preparing for Red Team Testing is determining what the organization wants to learn from the assessment.
Objectives should be specific and aligned with business risks.
Organizations may want to evaluate:
- Detection and response capabilities
- Security monitoring effectiveness
- Identity and access controls
- Network segmentation
- Protection of critical assets
- Incident response procedures
- Security team readiness
Clearly defined objectives help the red team design realistic attack scenarios and ensure the assessment measures outcomes that matter to the organization.
Set the Scope
The next step is to establish the scope of the Red Team Assessment.
The scope should clearly identify which systems, applications, networks, locations, and other assets are authorized for testing.
Organizations should define:
- In-scope systems and assets
- Out-of-scope systems
- External and internal environments
- Authorized attack scenarios
- Testing timeframes
- Sensitive systems requiring additional restrictions
A clearly documented scope prevents misunderstandings and ensures that testing remains controlled and authorized.
Prepare Systems
Before the assessment begins, technical teams should ensure that critical systems are properly prepared.
This does not mean disabling security controls. In fact, the objective of a red team exercise is to evaluate how existing defenses perform under realistic conditions.
Organizations should verify that:
- Critical systems are backed up where appropriate
- Security monitoring is operational
- Logging is enabled
- Endpoint security controls are functioning
- Important assets are properly identified
- Emergency contacts are available
- Business-critical operations are protected
The organization should also ensure that relevant security teams understand their responsibilities during the engagement.
Establish Rules of Engagement
Rules of engagement are a critical part of Red Team Penetration Testing.
They define how the assessment will be conducted and establish boundaries that protect the organization from unnecessary operational risk.
Rules should address:
- Authorized testing techniques
- Approved targets
- Testing windows
- Communication procedures
- Emergency escalation contacts
- Activities that are prohibited
- Data-handling requirements
- Conditions for stopping the assessment
These rules allow the red team to simulate realistic attacks while maintaining appropriate safety and operational controls.
Prepare Monitoring & Detection
A red team exercise is not only about whether attackers can compromise systems. It is also about whether defenders can detect and respond to their activity.
Before testing begins, organizations should verify that monitoring systems are collecting relevant security events.
Security teams should review:
- SIEM monitoring
- Endpoint detection and response
- Network monitoring
- Identity and authentication logs
- Cloud security monitoring
- Alerting mechanisms
- Incident-response workflows
Avoiding unnecessary changes to detection controls during the assessment can provide a more accurate picture of the organization's existing defensive capabilities.
Conduct the Assessment
Once objectives, scope, systems, rules, and monitoring are ready, the Cybersecurity Assessment can begin.
The red team operates according to the agreed rules of engagement and attempts to achieve the defined objectives using realistic attack scenarios.
During the engagement, defenders may or may not be informed about the specific activities, depending on the assessment design.
This approach can help measure:
- How quickly suspicious activity is detected
- Whether alerts reach the appropriate teams
- How effectively incidents are investigated
- Whether escalation procedures work
- Whether security controls prevent further compromise
The goal is to generate realistic security insights rather than simply identify individual vulnerabilities.
Remediation
The final stage is turning assessment findings into security improvements.
A comprehensive report should document:
- Attack paths
- Security weaknesses
- Detection gaps
- Control failures
- Potential business impact
- Evidence and observations
- Recommended remediation
Security teams should prioritize findings based on risk and business impact. After remediation, organizations may conduct retesting to verify that identified weaknesses have been addressed effectively.
Conclusion
Preparing for a Red Team Assessment requires more than scheduling a penetration testing engagement. Organizations need clearly defined objectives, a controlled scope, properly prepared systems, documented rules of engagement, effective monitoring, and a structured remediation process.
When properly planned, Red Team Testing can provide valuable insight into how an organization might withstand a realistic cyberattack.