Common Security Gaps That Zero Trust Can Help Address
By: Ganesan D
7 Oct 2026
Category:
Cyber Security
Introduction
Traditional security models often rely on the assumption that users and devices inside a corporate network can be trusted. However, modern businesses operate across cloud platforms, remote work environments, SaaS applications, and personal or unmanaged devices, making this approach increasingly difficult to secure.
Zero Trust follows a different security philosophy: users, devices, and applications should not automatically be trusted simply because they are inside a network. Every access request should be appropriately verified and continuously evaluated.
Understanding common security gaps can help organizations determine how Zero Trust Implementation can strengthen their overall cybersecurity strategy.
Common Security Gaps
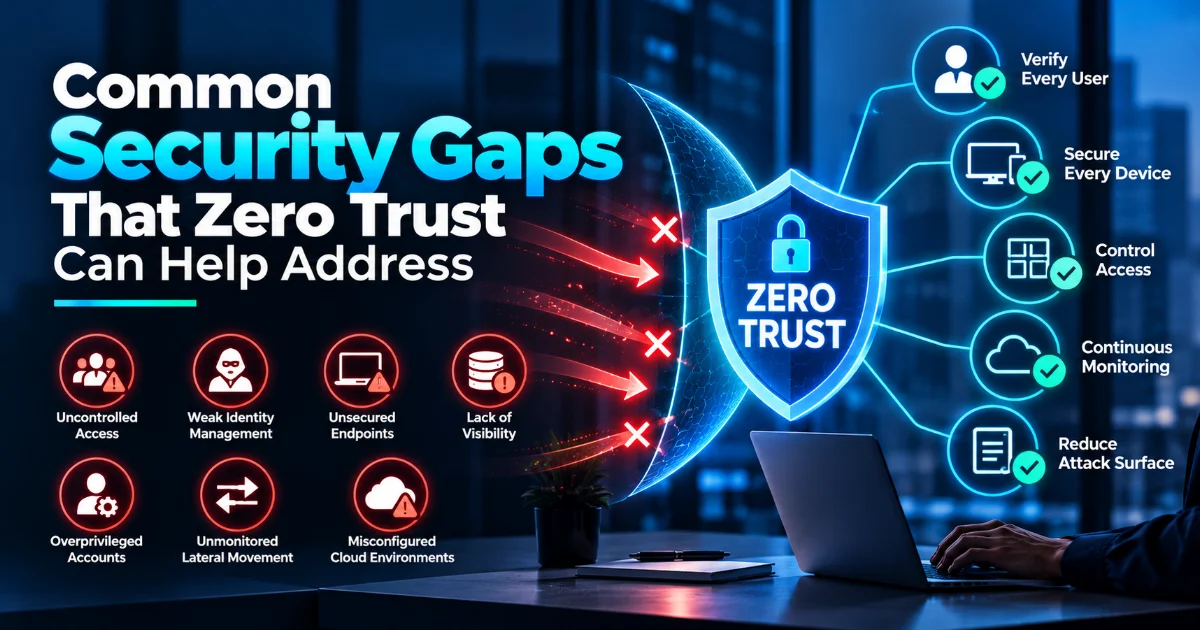
Organizations may face several weaknesses that traditional security approaches do not adequately address.
Excessive Access Privileges
Users may have access to more applications, systems, or data than they actually need. Compromised accounts can therefore provide attackers with opportunities for lateral movement.
Weak Identity Controls
Passwords alone may not provide sufficient protection against credential theft, phishing, and account compromise.
Unmanaged Devices
Employees may access business resources from devices that lack appropriate security controls, updates, or endpoint protection.
Limited Visibility
Security teams may have difficulty identifying unusual access activity when monitoring is fragmented across different systems.
Implicit Trust
Once a user or device has gained network access, traditional architectures may provide broader access than necessary.
These gaps can increase the potential impact of compromised credentials or devices.
Zero Trust Principles
Zero Trust is based on principles designed to reduce unnecessary access and limit the potential impact of security incidents.
Key principles include:
-
Verify explicitly
-
Apply least-privilege access
-
Assume breach
-
Continuously evaluate access
-
Protect resources rather than relying only on network boundaries
These principles can help organizations move from broad network-based trust toward more granular access controls.
Identity Verification
Strong identity verification is a fundamental part of Zero Trust Implementation.
Organizations can strengthen identity security by using:
-
Multi-factor authentication
-
Strong authentication policies
-
Conditional access controls
-
Identity-based authorization
-
Risk-based authentication
Access decisions can consider factors such as user identity, device status, location, application, and risk level.
Least Privilege
Least privilege ensures that users and systems receive only the access required to perform their responsibilities.
During Implementing Zero Trust, organizations should regularly review permissions and remove unnecessary access.
This can help reduce the potential impact of compromised accounts and limit unauthorized movement between systems.
Device Security
A Zero Trust strategy should also consider whether a device is secure before granting access.
Organizations can evaluate:
-
Device identity
-
Operating system status
-
Security configuration
-
Endpoint protection
-
Patch status
-
Device compliance
Access can then be restricted when a device does not meet the organization's security requirements.
Continuous Monitoring
Zero Trust does not end after a user successfully authenticates. Access and activity should continue to be evaluated based on changing risk conditions.
Security teams can monitor:
-
Authentication activity
-
Access to sensitive resources
-
Unusual user behavior
-
Device security events
-
Privilege changes
-
Application activity
Continuous monitoring can help organizations identify suspicious behavior and respond before an incident becomes more serious.
How to Implement Zero Trust
Organizations wondering How to Implement Zero Trust should begin with a phased approach.
1. Identify Critical Assets and Resources
Determine which applications, systems, and data require stronger protection.
2. Understand Users and Devices
Create visibility into who is accessing resources and from which devices.
3. Strengthen Identity Controls
Implement MFA, conditional access, and appropriate authentication policies.
4. Apply Least Privilege
Limit access based on job requirements and business needs.
5. Enforce Device Security
Require devices to meet defined security and compliance standards.
6. Monitor Continuously
Collect and analyze security events to identify unusual activity.
7. Review and Improve
Regularly assess access policies, security controls, and emerging risks.
Conclusion
Common security gaps such as excessive privileges, weak identity controls, unmanaged devices, limited visibility, and implicit network trust can increase an organization's exposure to cyber threats.
Zero Trust Implementation helps address these weaknesses by requiring stronger identity verification, enforcing least-privilege access, evaluating device security, and continuously monitoring activity.
Organizations should approach Zero Trust Implementation as an ongoing security strategy rather than a single technology deployment. By gradually implementing Zero Trust principles across identities, devices, applications, and data, businesses can strengthen access security and reduce the potential impact of compromised accounts or devices.