Container Security: Protecting Docker and Kubernetes Environments
By: Ganesan D
30 Oct 2026
Category:
Cyber Security
Introduction
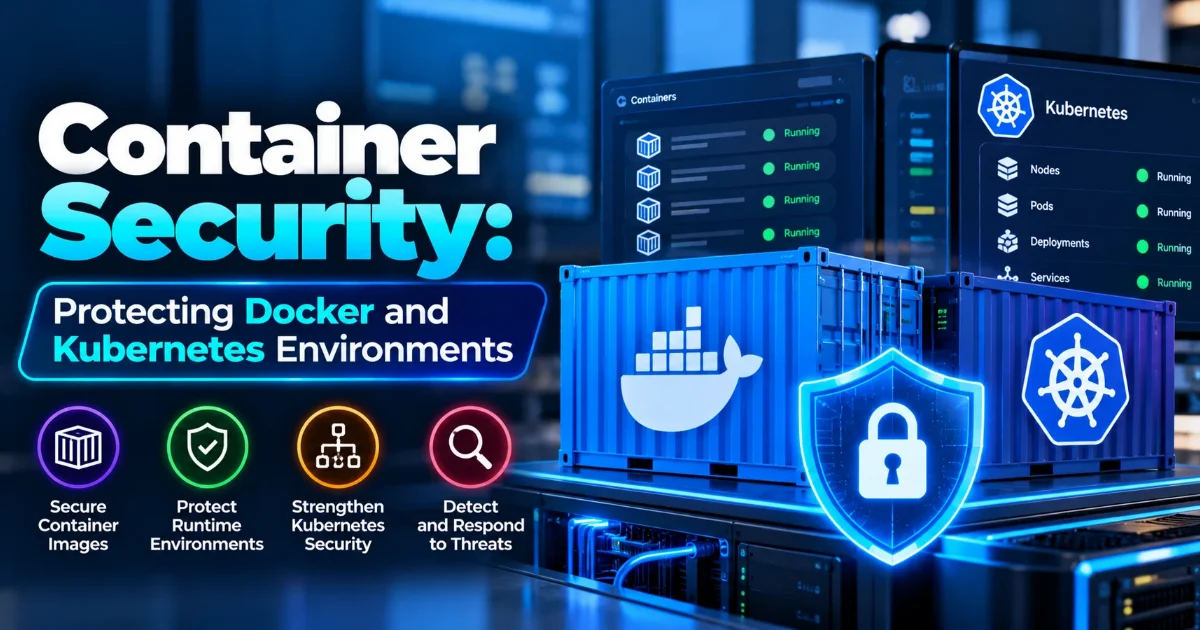
Containers help businesses develop, deploy, and scale applications efficiently. Technologies such as Docker and Kubernetes support modern cloud-native environments, but insecure images, excessive permissions, and misconfigured workloads can expose applications to cyber threats. Effective container security helps organisations protect applications throughout development and deployment.
What Is Container Security?
Container security involves protecting container images, runtime environments, orchestration platforms, and the infrastructure supporting containerised applications. It includes vulnerability scanning, access control, configuration management, and runtime monitoring.
Businesses investing in container security in the UAE can reduce risks across their cloud-native environments and strengthen application security.
Understanding Docker and Kubernetes Environments
Docker provides tools to build, package, and run applications in containers. Kubernetes orchestrates containers across clusters, managing deployment, scaling, networking, and recovery.
Both technologies require security controls. Docker environments need secure images and container configurations, while Kubernetes environments also require protected cluster components, workload permissions, network policies, and secure access to the control plane.
Common Container Security Risks
Containerised environments may face several security challenges:
-
Vulnerable Images:
Outdated libraries and operating system packages may contain known vulnerabilities.
-
Misconfigurations:
Unnecessary services, exposed ports, and insecure defaults can increase attack surfaces.
-
Excessive Privileges:
Containers running as root or with broad permissions may increase the impact of compromise.
-
Exposed Secrets:
API keys and passwords embedded in images or deployment files can be stolen.
-
Insecure Orchestration:
Weak Kubernetes access controls and unrestricted network communication may enable lateral movement.
-
Supply Chain Attacks:
Malicious or compromised images can introduce threats into production systems.
Vulnerable Images and Misconfigurations
Container images can contain vulnerable dependencies even when the application code is secure. Businesses should scan images before deployment, use trusted base images, remove unnecessary packages, and rebuild images regularly.
Configuration reviews should identify privileged containers, unnecessary capabilities, excessive permissions, exposed management interfaces, and insecure storage settings. A Docker security assessment in the UAE can help identify weaknesses in image builds, container configurations, and deployment practices.
Container Security Tools
Organisations can use different tools to strengthen protection:
-
Trivy:
Scans container images and other software artefacts for vulnerabilities and misconfigurations.
-
Docker Scout:
Helps analyse image contents and identify known vulnerabilities.
-
Kubescape:
Assesses Kubernetes environments against security frameworks and configuration checks.
-
Falco:
Supports runtime threat detection by monitoring system and workload activity.
Tool selection should reflect the organisation's architecture, operational needs, and existing security processes.
Protecting Containers Across the Application Lifecycle
Security should be integrated into every stage of application delivery:
-
Development:
Scan dependencies and prevent secrets from entering source code.
-
Build:
Use trusted base images and generate software component inventories where appropriate.
-
Testing:
Run vulnerability and configuration assessments before release.
-
Deployment:
Apply least-privilege access, image verification, and Kubernetes security policies.
-
Runtime:
Monitor suspicious behaviour, restrict network communication, and respond to alerts.
-
Maintenance:
Patch vulnerabilities and regularly review permissions and configurations.
Professional cloud container security services in Dubai can help businesses assess these controls and integrate security into development and operations workflows.
Container Security Best Practices
Organisations can strengthen container security by following these best practices:
-
Use Trusted Images:
Use minimal, trusted, and regularly updated images to reduce vulnerabilities.
-
Avoid Running Containers as Root:
Configure containers to use non-root users wherever possible.
-
Enforce Least Privilege:
Apply restricted permissions and Kubernetes role-based access control (RBAC).
-
Secure Sensitive Information:
Store API keys, passwords, and other credentials in dedicated secrets management systems.
-
Apply Network Segmentation:
Use network restrictions and Kubernetes network policies to control workload communication.
-
Monitor Containers Continuously:
Scan images regularly and monitor running workloads for suspicious activity.
-
Prepare for Security Incidents:
Maintain tested backups and incident response procedures to minimise the impact of security incidents.
Frequently Asked Questions
1. Why Is Container Security Important?
Container security helps prevent vulnerabilities, misconfigurations, and compromised workloads from affecting business applications. It also protects sensitive data and strengthens cloud-native infrastructure.
2. How Often Should Containers Be Assessed?
Scan images during development and before deployment, and reassess environments regularly as dependencies and configurations change. Continuous monitoring also helps identify newly discovered vulnerabilities and suspicious runtime activity.
3. What Does a Container Security Assessment Include?
A container security assessment in the UAE may review image vulnerabilities, Docker configurations, Kubernetes permissions, network policies, secrets handling, and runtime monitoring.
Conclusion
Securing Docker and Kubernetes environments requires continuous vulnerability management, secure configurations, controlled access, and runtime monitoring. Integrating these measures throughout the application lifecycle helps reduce risks and protect cloud-native workloads.
Strengthen Your Container Security with Agan Cyber Security LLC
Strengthen your container security with Agan Cyber Security LLC. Our cybersecurity services can help identify vulnerabilities, assess cloud-native environments, and improve application security.
Contact our team to discuss container security requirements in Dubai and across the UAE.
Contact us today to discuss your container security requirements.