How Businesses Can Identify and Fix Cybersecurity Vulnerabilities
By: Ganesan D
22 Sep 2026
Category:
Cyber Security
Introduction
Businesses rely on digital systems, applications, networks, cloud platforms, and connected devices to support their daily operations. While these technologies improve efficiency, they can also introduce security weaknesses that attackers may attempt to exploit.
Cybersecurity vulnerabilities can exist in software, hardware, applications, configurations, user accounts, networks, and business processes. If these weaknesses remain unidentified or unaddressed, they can increase the organization's exposure to cyber threats.
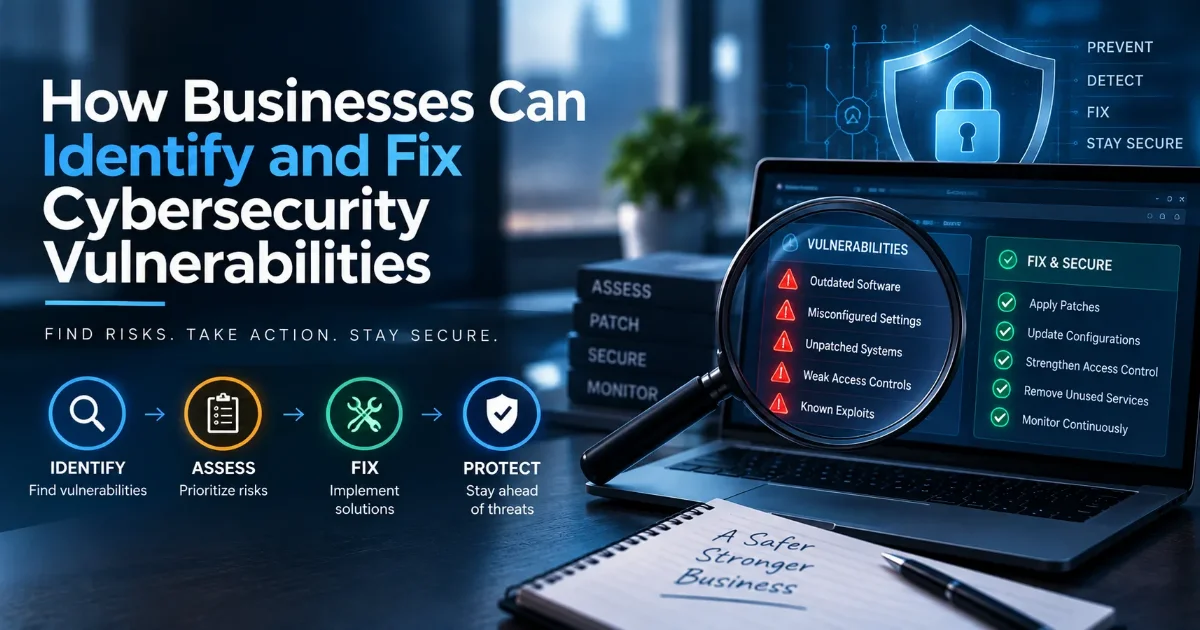
A structured Vulnerability Assessment helps businesses discover potential security weaknesses, while a Cybersecurity Risk Assessment helps determine which vulnerabilities require the most urgent attention. Effective Vulnerability Management then provides a continuous process for identifying, prioritizing, remediating, and monitoring vulnerabilities.
Common Cybersecurity Vulnerabilities
Cybersecurity vulnerabilities can take many forms depending on an organization's technology environment.
Common examples include:
✔ Outdated software and operating systems
✔ Missing security patches
✔ Weak passwords and authentication controls
✔ Misconfigured cloud or network services
✔ Excessive user privileges
✔ Insecure applications and APIs
✔ Unnecessary exposed services
✔ Vulnerable third-party components
✔ Poorly protected sensitive data
✔ Inadequate security configurations
Not every vulnerability presents the same level of risk. The potential impact depends on factors such as exploitability, affected assets, exposure, and the sensitivity of the information involved.
How to Identify Vulnerabilities
The first step in managing vulnerabilities is discovering where they exist.
Businesses can use a combination of automated tools and expert-led security assessments.
Vulnerability Scanning
Automated vulnerability scanning can examine systems, applications, networks, and devices for known security weaknesses.
It can help identify:
✔ Missing patches
✔ Outdated software
✔ Known vulnerabilities
✔ Configuration weaknesses
✔ Exposed services
✔ Security misconfigurations
Manual Security Assessment
Automated scanning should be complemented by manual analysis where appropriate. Security professionals can validate findings, investigate application-specific issues, and identify weaknesses that automated tools may not detect effectively.
A combination of automated scanning and expert analysis can provide broader security visibility.
Cybersecurity Risk Assessment
Finding vulnerabilities is only part of the process. Organizations also need to understand which vulnerabilities represent the greatest business risk.
A Cybersecurity Risk Assessment can consider:
✔ Severity of the vulnerability
✔ Likelihood of exploitation
✔ Internet exposure
✔ Importance of the affected asset
✔ Sensitivity of affected data
✔ Potential operational impact
✔ Existing security controls
For example, a vulnerability affecting an isolated test system may require a different response from a similar vulnerability affecting a publicly accessible production server containing sensitive business information.
Risk assessment helps organizations make informed remediation decisions.
Fix and Prioritize Vulnerabilities
Businesses may discover hundreds or even thousands of potential vulnerabilities during an assessment. Attempting to fix everything simultaneously may not be practical.
This is where Vulnerability Management becomes important.
Organizations can prioritize vulnerabilities based on factors such as:
✔ Criticality and severity
✔ Exploit availability
✔ Asset importance
✔ External exposure
✔ Business impact
✔ Availability of security patches
✔ Existing compensating controls
A structured remediation process can follow:
Identify → Validate → Prioritize → Remediate → Verify
High-risk vulnerabilities affecting critical or exposed systems should generally receive appropriate attention based on the organization's risk-management process.
Vulnerability Remediation
Once vulnerabilities have been prioritized, organizations can determine the appropriate remediation action.
Depending on the finding, remediation may include:
✔ Applying security patches
✔ Updating vulnerable software
✔ Changing insecure configurations
✔ Strengthening authentication
✔ Restricting unnecessary access
✔ Removing exposed services
✔ Fixing application code
✔ Improving network segmentation
✔ Updating security policies
In some cases, an immediate permanent fix may not be possible. Organizations can implement compensating controls to reduce exposure while a permanent remediation is planned.
After remediation, validation or retesting should be performed to confirm that the vulnerability has been properly addressed.
Continuous Monitoring
Cybersecurity vulnerabilities are not a one-time problem. New vulnerabilities can emerge when software is updated, new systems are deployed, configurations change, or new threats are discovered.
Continuous Vulnerability Management helps organizations maintain visibility over their changing technology environment.
Organizations should consider:
✔ Regular vulnerability scanning
✔ Patch management
✔ Asset inventory management
✔ Continuous security monitoring
✔ Periodic penetration testing
✔ Configuration reviews
✔ Remediation tracking
✔ Regular risk assessments
Continuous monitoring allows security teams to identify new weaknesses and respond before they become larger security problems.
Conclusion
A comprehensive Vulnerability Assessment helps identify weaknesses, while a Cybersecurity Risk Assessment provides context for understanding their potential business impact. Effective Vulnerability Management then ensures that identified issues are tracked and addressed over time.